Business Law / Ontario
Business compliance, privacy and technology agreements
Understand the legal requirements behind your operations, customer information and technology. We help Ontario businesses review policies, agreements and practical next steps.
Legal services provided by a lawyer licensed in Ontario.
- Clear advice
- Practical next steps
- Steady guidance
What is changing in your business?
Review operational legal requirements
You are starting, expanding or changing operations and need to identify relevant requirements and priorities.
Prepare privacy or customer-facing terms
You want policies, website terms or e-commerce agreements that reflect how your business handles information and customers.
Assess a technology provider or AI tool
You are reviewing software, vendor terms, data permissions, confidentiality or internal AI-use rules.
Choose the legal work that fits
A legal review, technical security assessment and operational implementation address different questions. We explain the proposed work and any additional expertise needed.
Start with what your business does, what you are introducing or reviewing, and the decision you need to make. A brief outline is enough.
Start with the activities your business actually carries on
The requirements to consider depend on your operations, industry, customers and where you do business. A useful review begins by defining those facts.
We assist with legal risk assessments, compliance audits and reviews of applicable regulatory and industry requirements within an agreed scope. Describe the products or services you offer, the locations involved, your role and any change you are planning.
Set the boundaries of the review
A focused assessment might concern a new customer process, an online service, a technology rollout or a group of business policies. We identify the documents and questions to be considered, the proposed deliverable and the issues requiring separate advice. A review of one process does not establish compliance across the entire business.
Documents we can discuss
- Existing policies, procedures and relevant notices
- Privacy policies, website terms and e-commerce agreements
- AI-use policies and internal technology rules
- Software, cloud and other technology vendor agreements
- Confidentiality, data-use and digital-content licence terms
Turn findings into defined next steps
The agreed work may include advice on identified gaps, proposed document changes, contractual negotiations or a plan for connected professional input. We can also discuss ongoing counsel for contracts, governance and compliance as the business changes.
Connect privacy and customer-facing terms with real practices
A policy needs to describe how information is handled. Website and e-commerce terms address a different part of the customer relationship.
We can draft or review privacy policies, website terms and e-commerce agreements in the context of your operations. Explain what information is collected, why it is needed, who uses it, which providers receive it and how customers interact with the business.
Assess the applicable privacy framework
The federal Personal Information Protection and Electronic Documents Act (PIPEDA) generally applies to personal information handled in commercial activities, subject to its scope and exceptions. Other laws may apply to particular information, sectors or jurisdictions. The relevant rules need assessment before relying on a general template.
Make the documents work together
Privacy notices, consent processes and internal practices should be considered together. Customer-facing terms may also need to address the service or product, order acceptance, payment, cancellation, permitted use and responsibility for content. The appropriate provisions depend on the transaction and applicable requirements.
Read technology commitments alongside information and ownership rights
The software licence, vendor terms and internal use policy should be considered with the way the tool will operate in your business.
We can review software and technology vendor agreements, confidentiality obligations, permitted data-use terms and internal AI-use policies. Identify the tool, its intended users and the broad categories of information involved without sending sensitive datasets in your first inquiry.
Clarify what the provider may do
Contract questions may include service scope, licences, access rights, data uses, subcontractors, storage locations, support, fees, renewals, liability, notice of incidents and the return or deletion of information when the relationship ends. Contract terms and a provider’s actual practices both matter.
Set internal rules for AI tools
An AI-use policy can address approved tools and uses, confidential or personal information, human review, staff responsibilities and escalation of concerns. We consider the proposed legal rules with the provider’s terms and the business use case. Legal obligations continue to need assessment when AI is involved.
Digital content, software, inputs and outputs can also raise ownership and licensing questions. We help document the relevant commercial rights and identify where connected intellectual property strategy or other advice is needed; ownership or permission should not be assumed from access to a tool.
Questions to bring into the review
Activities and applicable requirements
The business process, industry, parties, jurisdictions and the legal questions to be assessed.
Information and permitted uses
What is collected, the purposes, access and disclosure arrangements, retention and relevant consent processes.
Customer and website commitments
How the service is offered, customer terms, order and payment processes, notices and applicable protections.
Vendor responsibilities
Service scope, subcontractors, data handling, support, incident notice, liability and changes to the terms.
AI, content and commercial rights
Approved uses, confidential inputs, human review, licences and rights in software or digital material.
Implementation and ongoing review
Who carries out the agreed changes, staff responsibilities, updates, renewals and separate professional input.
The priorities depend on the actual business and engagement. Documents should be reviewed when relevant operations, providers or legal requirements change.
Meet our principal lawyer
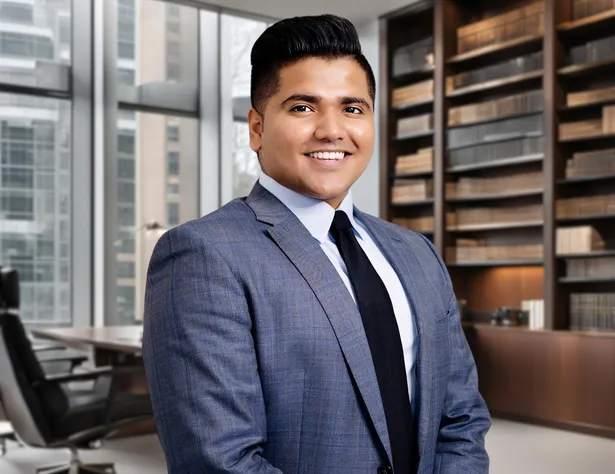
Vinay Thapliyal
Founder & Principal Lawyer
Licensed to practise law in Ontario
Legal Route’s business contract, governance and ongoing counsel services allow policies and technology commitments to be considered alongside the wider commercial relationship and the need for additional professional advice.
Meet Vinay ThapliyalTell us what your business is introducing or reviewing
A short description is enough for your first inquiry.
What to tell us
- Business and people involved
Your business name, your role, the industry and the names of relevant vendors or other parties.
- The process or technology
What you do, what is changing and the broad kinds of information or technology involved.
- Documents and assistance
Whether policies or contracts already exist and whether you need advice, document preparation, review or negotiation.
- Dates and existing concerns
Any proposed launch, renewal, signing or response date, and whether a complaint, notice or incident already exists.
Consultation, fees and scope
Fees depend on the scope, documents, complexity and assistance required. We confirm any consultation fee before booking and explain proposed fees, taxes and anticipated expenses before retention.
Technical assessments, implementation and advice in another sector or jurisdiction may require separate arrangements.
Please wait for our secure document-sharing instructions before sending customer records, credentials, confidential policies, contracts or incident details.
How engagement begins
Confirm whether we can assist
We obtain the information needed to check conflicts, identify the issue and assess availability.
Define the review and deliverables
We discuss the relevant documents, proposed scope, consultation arrangements, fees, taxes and expenses.
Carry out the agreed work
Once retained, we provide the agreed advice, policy or contract work, negotiations or ongoing support.
Questions about business compliance and technology
Can you help identify which legal requirements apply to our business?
We can discuss a defined legal risk or compliance review based on your activities, industry, information and jurisdictions. The engagement identifies the questions and documents to be assessed. Sector-specific, technical or other-jurisdiction work may require additional advice.
Can we use a general privacy policy or website terms template?
A template needs to be assessed against your actual practices and applicable requirements. Privacy policies, consent processes and website or e-commerce terms serve different purposes. We can discuss preparing or adapting documents around the way your business operates.
Can you review a cloud software or technology vendor agreement?
Yes, subject to conflicts and the agreed scope. We can discuss the service and licence terms, confidentiality, data-use permissions, responsibilities, liability, renewal and exit provisions. Technical capabilities and security controls may require separate assessment.
Can you help prepare rules for staff using AI tools?
We can discuss an AI-use policy addressing approved uses, information restrictions, human review and staff responsibilities. The work should reflect the tools, provider terms and business use case. A policy needs appropriate implementation and does not establish every tool’s legality, security or accuracy.
Does having a privacy policy permit us to send marketing emails or texts?
A privacy policy alone does not determine that. CASL requirements for commercial electronic messages, including consent, identification, unsubscribe arrangements and any applicable exception, need separate consideration. We can discuss the proposed communications and related practices within an agreed review.
Does a legal review certify our cybersecurity or overall compliance?
No. The legal review addresses its agreed scope and the information available. Technical security testing, certifications and operational implementation involve different work. We explain relevant limitations and when other qualified advisers are needed.
What if a complaint, notice or information incident has already occurred?
Mention the issue and any actual dates at the outset. Response work may need a separate scope and additional advisers. Wait for secure-sharing instructions before sending sensitive details. An inquiry does not confirm that we are acting or can protect a deadline.
Serving clients across Ontario
Virtual appointments available · In-person appointments in Brampton
We explain identification, secure document delivery and any signing or attendance requirements. Operations, information or counterparties outside Ontario may require advice in another jurisdiction.
This page provides general legal information, not advice for your circumstances. Sending an inquiry does not, by itself, create a lawyer-client relationship or confirm acceptance of your matter or deadline.